FORT HUACHUCA, Ariz. — For more than two decades, the Communications-Electronics Command’s U.S. Army Information Systems Engineering Command has supported Army cybersecurity engineering. During this time, USAISEC has drawn on extensive institutional experience spanning the evolution of legacy security standards from the Department of Defense Information Technology Security Certification and Accreditation Process and the DoD Information Assurance Certification and Accreditation Process to today’s Risk Management Framework.
Now, USAISEC is drawing on its comprehensive cybersecurity engineering knowledge to provide an agile RMF as a Service model. The RMFaaS model is designed to support cybersecurity compliance and mission readiness across diverse Department of War systems, directly addressing the growing technical complexity of modern security standards and the shortage of specialized cybersecurity personnel. To bridge these operational gaps, USAISEC provides dedicated subject matter experts to fill critical compliance roles, such as information system security managers and authorizing official designated representatives, for organizations lacking sufficient organic resources.
Safeguarding critical facilities and joint infrastructure
Across military installations, the RMFaaS model delivers tangible results by securing information and operational technology environments.
At the enterprise level, USAISEC provides RMFaaS governance support for the Office of the Provost Marshal General Joint Analytic Real-Time Virtual Information Sharing System. As a web-based security management and threat-tracking platform, JARVISS protects installations and force elements globally. Maintaining a continuous authority to operate for JARVISS ensures installation commanders receive real-time situational awareness. Additionally, USAISEC applies RMFaaS governance to several fire and emergency services systems for OPMG. These physical security and life-safety networks represent operational technology, which requires specialized cybersecurity engineering compared to traditional desktop networks.
The reach of RMFaaS extends into joint military construction initiatives. USAISEC currently delivers direct cybersecurity engineering support to the Naval Facilities Engineering Systems Command for eight facility-related control systems at Walter Reed National Military Medical Center. This engineering effort supports a major ongoing military construction renovation at the hospital. By securing heating and cooling, utility monitoring, and building automation systems, USAISEC ensures joint medical personnel operate in a reliable, protected facility.
Cybersecurity engineering ultimately protects mission capability and warfighting readiness. Robert Little, USAISEC director of the Installation and Cyber Engineering Directorate, emphasized that operational readiness of Army commands increasingly depends on a resilient, secure infrastructure.
“Ensuring systems have a current, well-maintained authority to operate is critical for mission success,” said Robert. “The RMFaaS initiative is designed to provide that assurance, allowing commands to focus on their core missions while maintaining compliance with federal and DoW standards.”
Supporting the RMF lifecycle
The RMF lifecycle consists of seven structured steps: prepare, categorize, select, implement, assess, authorize, and monitor. Through this process, the RMF transforms cybersecurity from a static barrier into an adaptive process, allowing the DoW and its partners to field resilient systems that can withstand and recover from modern cybersecurity threats.
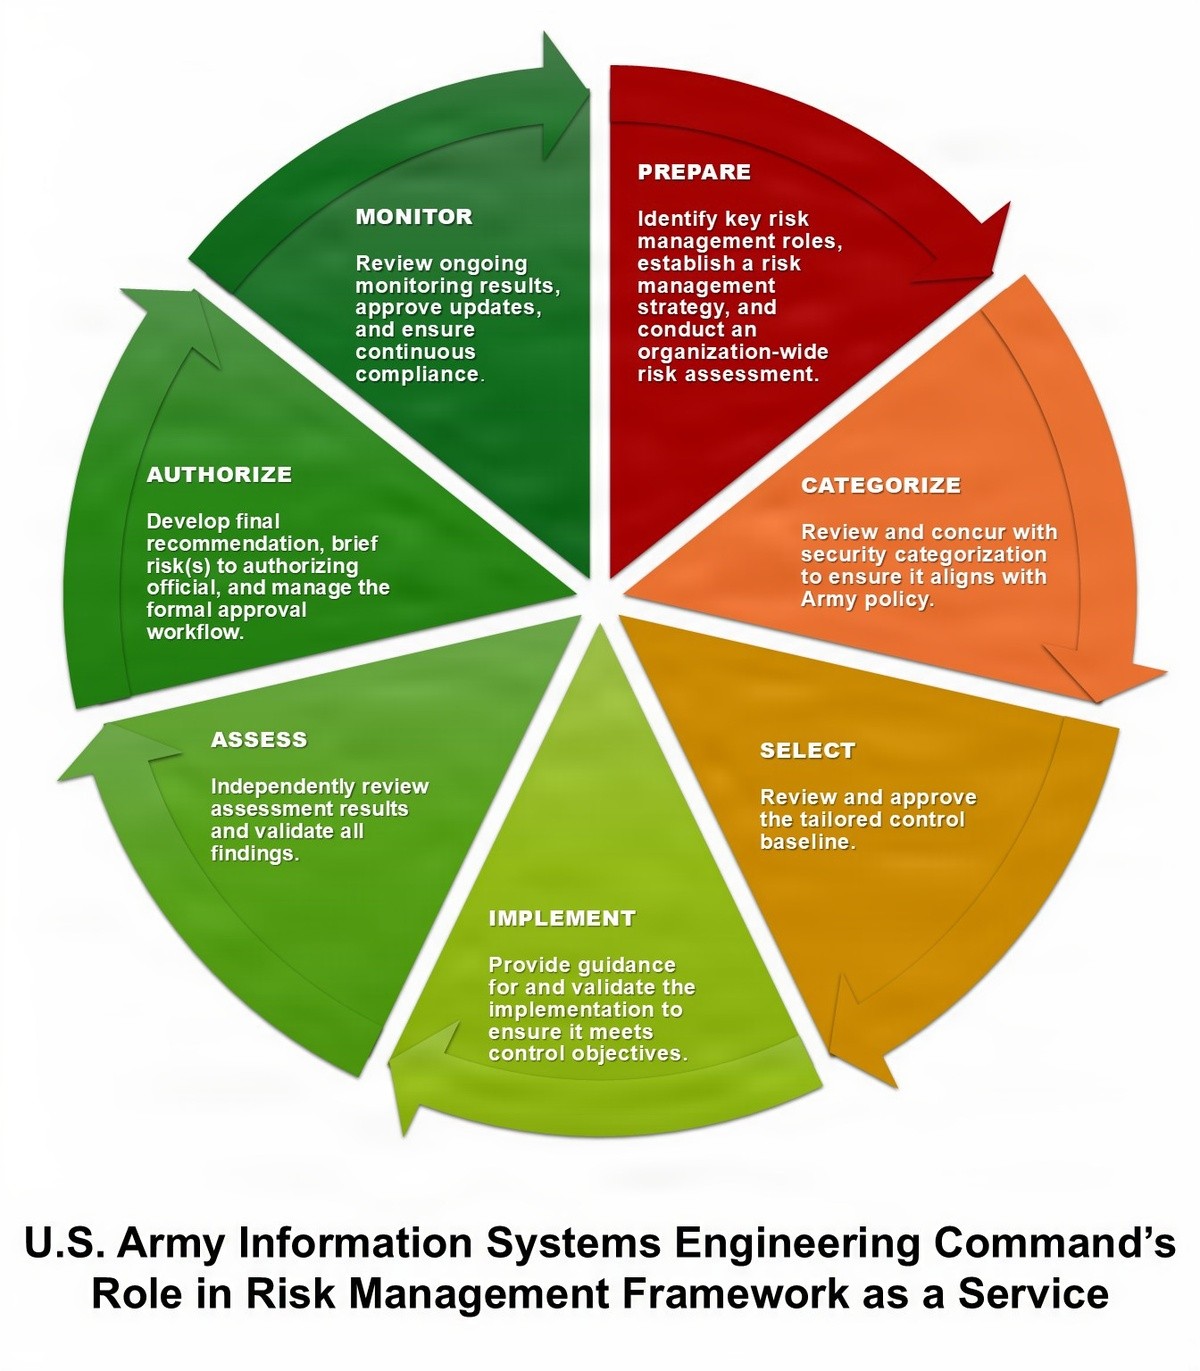
The RMFaaS model supports every phase of this lifecycle, from initial system categorization and security control assessment to continuous automated monitoring. This scalable, responsive service model delivers specialized cybersecurity expertise directly at the point of need, customized to each organization's distinct operational tempo. By pairing deep institutional knowledge with responsive service delivery, USAISEC’s RMFaaS model ensures the Army and broader joint force partners can neutralize emerging threats and sustain end-to-end military installation resilience.
For more information about the RMFaaS model or to inquire about other services and capabilities USAISEC provides for organizations, email USAISEC@Army.mil.
Social Sharing